Engineering Compliance Supply-chain Levels for Software Artifacts (SLSA) Is Your Source Code Secure? Chainloop Adds SLSA v1.2 Source Track Support
Cyber Resilience Act (CRA) Compliance Engineering From NYC to Europe: We're Bringing Our CRA Reference Implementation to the LF Roadshow
Engineering Compliance Security Introducing WebAssembly Policy Engine preview: Secure, Fast, and Language-Agnostic Compliance as Code
Changelog Engineering Compliance Changelog: AI-Driven Policy Authoring and Product Compliance at scale
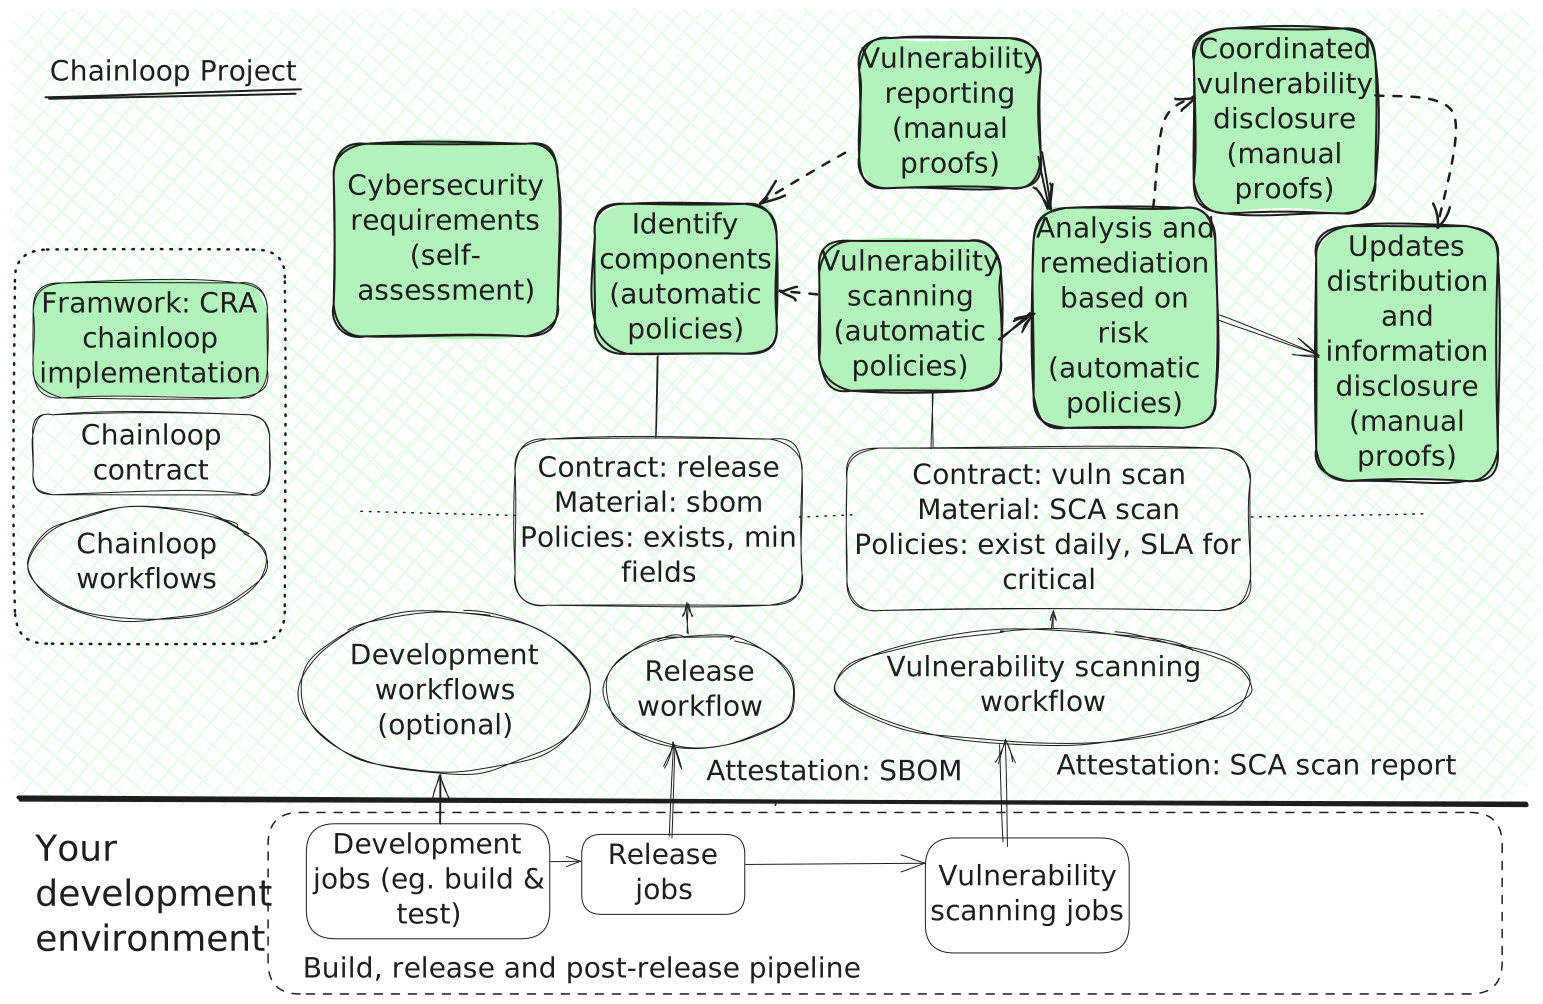
Engineering Compliance Cyber Resilience Act (CRA) Cyber Resilience Act: Your Action Plan - Part III: Chainloop, Your Launchpad for CRA Readiness
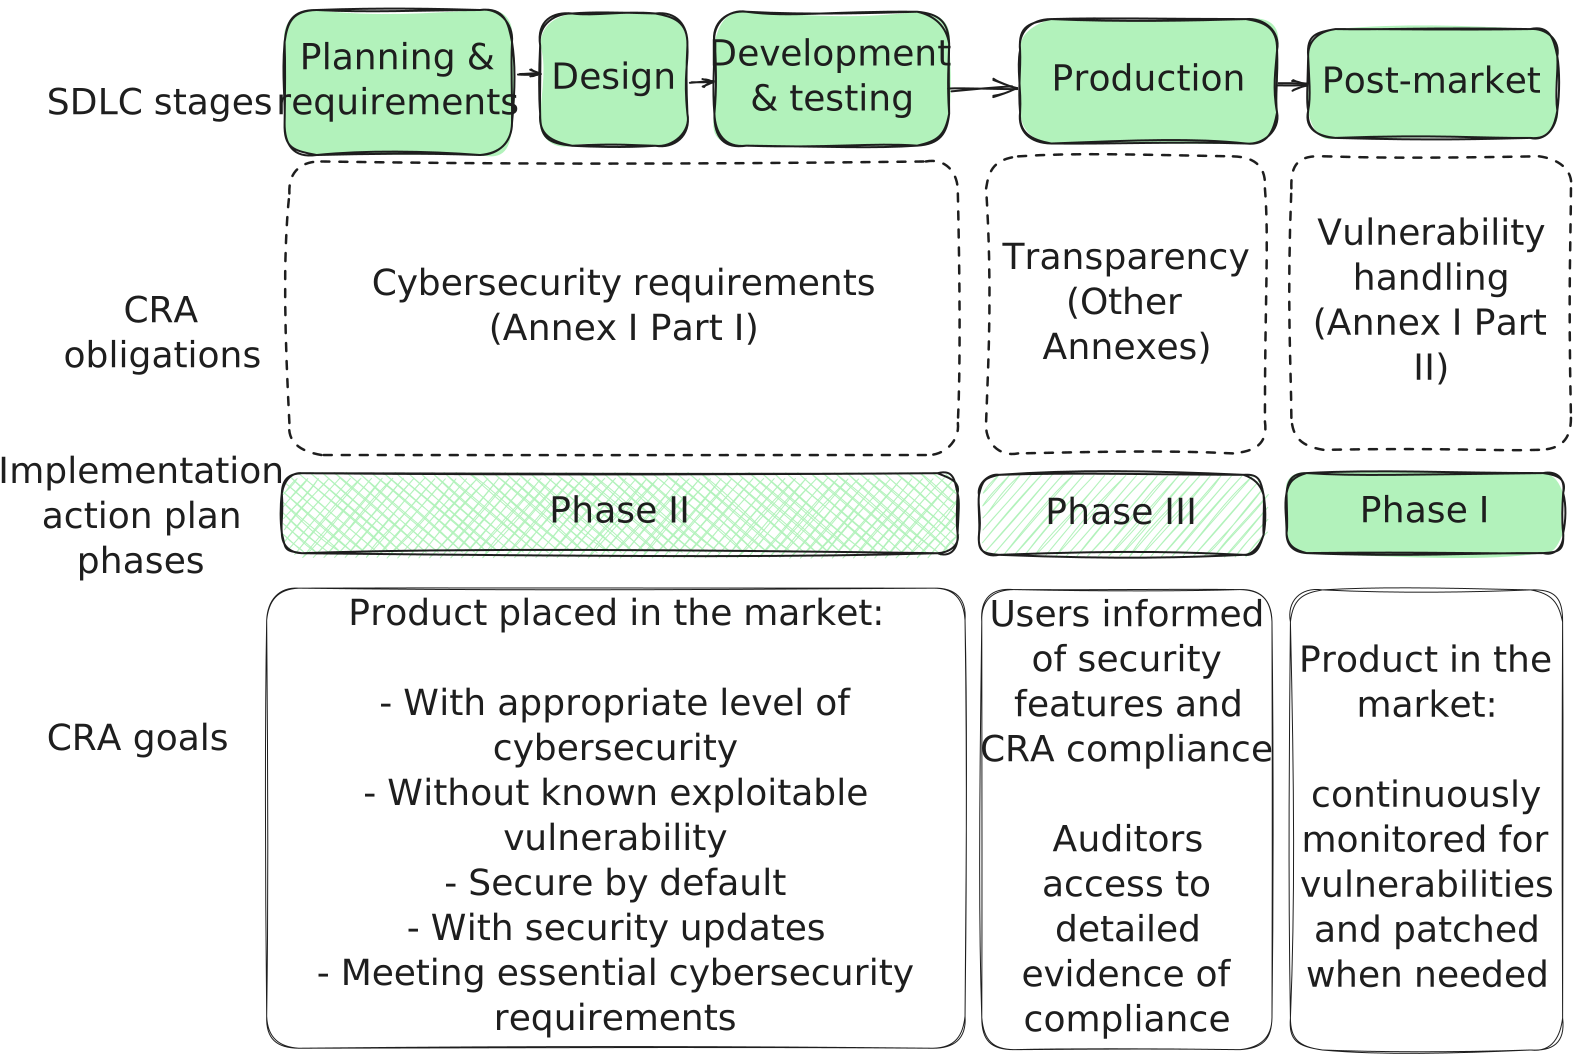
Engineering Compliance Cyber Resilience Act (CRA) Cyber Resilience Act: Your Action Plan - Part II: How to Break Down Your Compliance Strategy
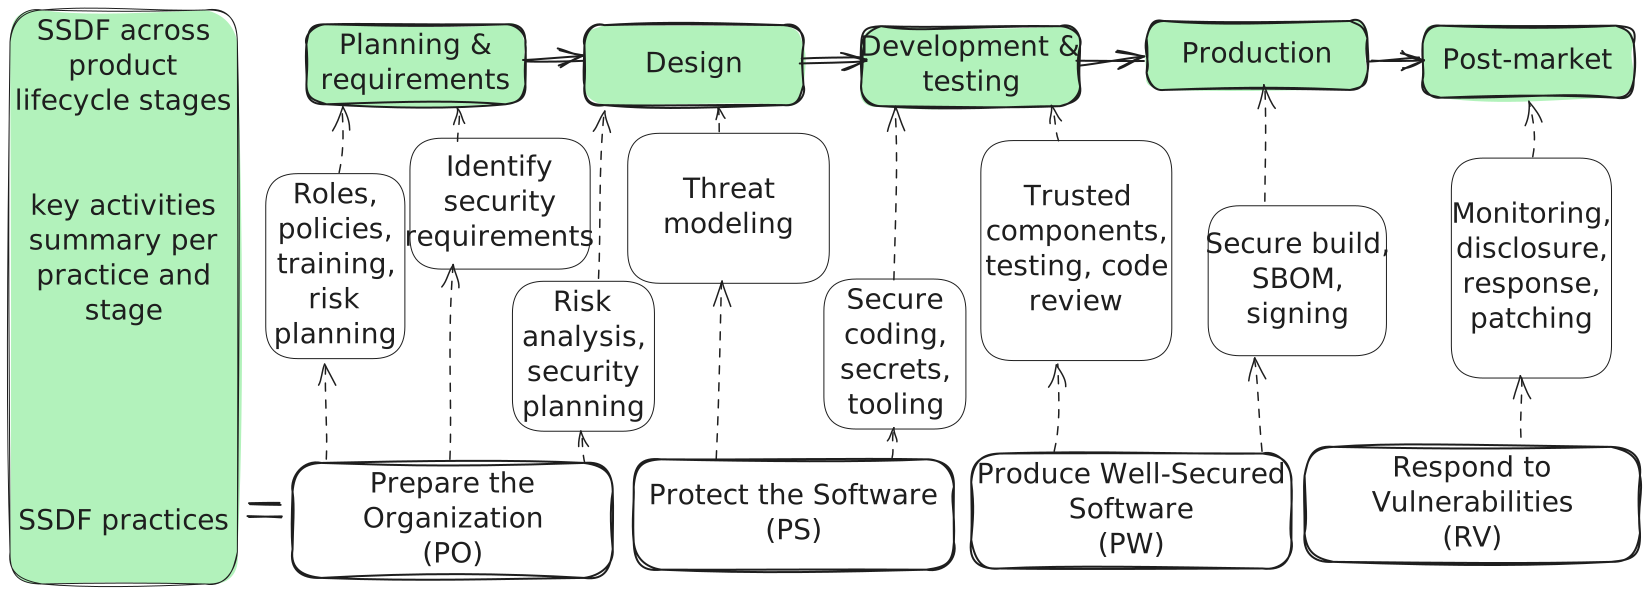
Engineering Compliance SSDF Building Secure Software by Design: SSDF Support Now in Preview on Chainloop
Engineering Compliance Cyber Resilience Act (CRA) Cyber Resilience Act: Your Action Plan - Part I: What You Need to Know and Why You Can’t Wait
Engineering Compliance Supply-chain Levels for Software Artifacts (SLSA) Securing the Software Supply Chain with SLSA and Chainloop